 TeamCare Managed IT
 TeamCare Cyber
 TeamCare Compliance
 AI Care
Managed IT, cybersecurity, and compliance working together.
TeamCare Compliance builds on TeamCare Cyber with the documentation, evidence, monitoring, and ongoing support needed to help regulated organizations stay secure and prepared.
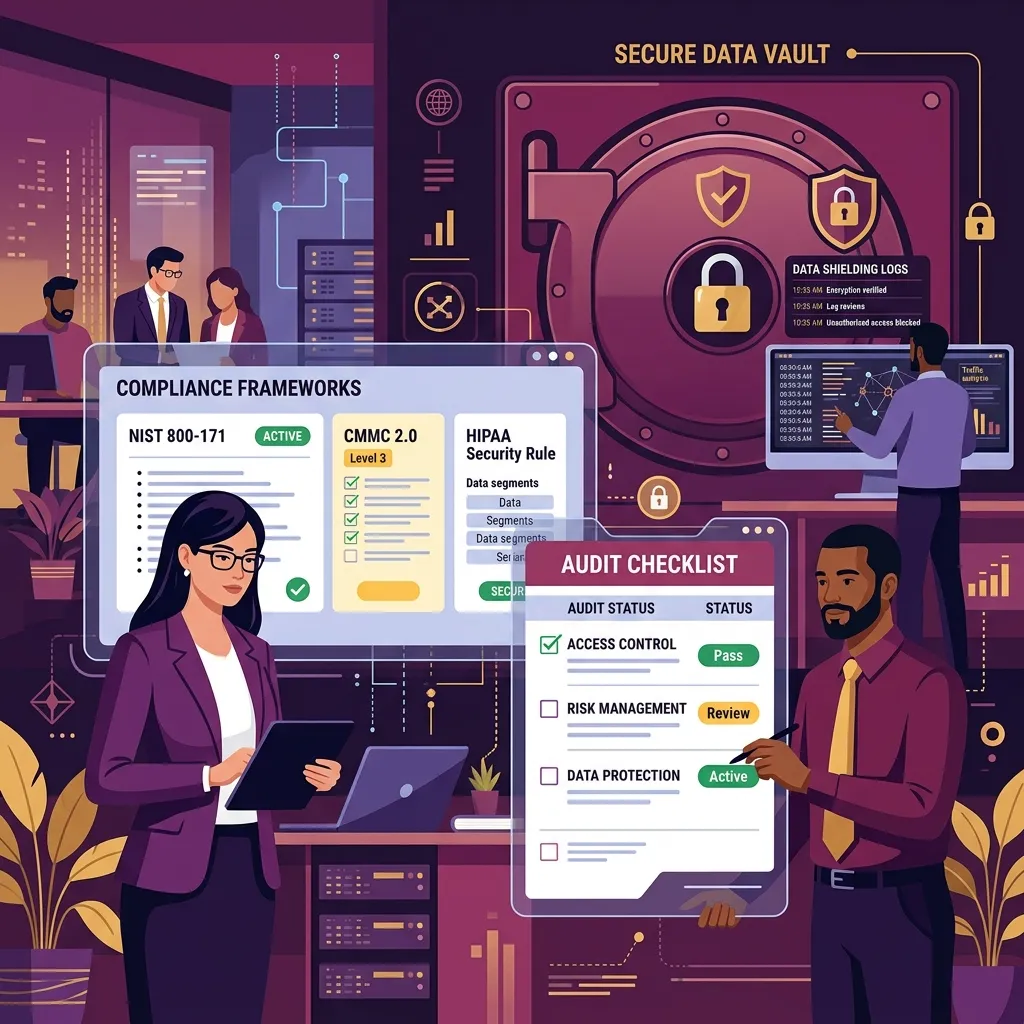
Defend It + Prove It
The TeamCare Cyber foundation plus the compliance layer.
- Managed IT + cybersecurity
- Compliance documentation & evidence
- Ongoing monitoring & reporting
- Audit and readiness support
Security is only part of the responsibility.
TeamCare Compliance is the compliance-focused level of Popper Tech Team’s Managed IT service. It includes the Managed IT and cybersecurity foundation of TeamCare Cyber, then adds the ongoing compliance layer needed by organizations with regulatory, contractual, or audit responsibilities.
For regulated businesses, having security controls in place is only part of the job. You may also need to show what controls exist, how they are managed, what evidence is being maintained, where gaps remain, and what actions are being taken to address them.
TeamCare Cyber - Defend It. TeamCare Compliance - Defend It + Prove It.
Compliance should not become a once-a-year scramble.
Audits, regulatory reviews, client requests, and insurance requirements can become stressful when documentation and evidence are scattered across different systems.
Security and Compliance Stay Connected
Technology, cybersecurity controls, monitoring, documentation, and compliance responsibilities are managed as connected parts of the same program.
Evidence Is Part of the Process
Documentation, evidence, reports, and records are maintained during normal operations rather than recreated after the fact.
Compliance Is Managed Continuously
Employees, technology, vendors, and risks change over time. Compliance needs to evolve alongside the business.
Practical Guidance Without Unnecessary Complexity
Understand what is required, what is already in place, where gaps exist, and what needs attention next.
TeamCare Cyber protects it. TeamCare Compliance helps prove it.
TeamCare Cyber
Managed IT + Cybersecurity
Manage and protect users, devices, systems, access, and data with proactive Managed IT and cybersecurity controls.
Defend It.
TeamCare Compliance
Managed IT + Cybersecurity + Compliance
Add ongoing compliance management, documentation, evidence, reporting, and audit readiness support.
Defend It + Prove It.
The TeamCare Cyber foundation plus ongoing compliance management.
TeamCare Compliance starts with everything your organization receives through TeamCare Cyber.
Managed IT & Cybersecurity Foundation
- 24/7 Managed IT support
- Proactive monitoring
- Patch and device management
- Network management
- Multi-Factor Authentication
- Endpoint Detection and Response
- Vulnerability management
- Privileged Access Management
- Security awareness training
- Security monitoring
- Technology reviews and planning
Compliance Layer
- Compliance audit maintenance
- Compliance documentation
- Record retention
- Security log retention
- Audit evidence management
- Security policy alignment
- Periodic compliance reporting
- Endpoint encryption
- Security information and event management
- Ongoing review against applicable standards
- Audit and assessment support
An initial compliance project may be required to establish the compliance service before ongoing maintenance begins.
Compliance is more than passing an audit.
Passing an audit is important. But compliance should not disappear from the priority list until the next review.
The goal is to know where you stand before someone asks.
Standards & Framework Alignment
Support for the requirements that apply to your organization.
Different industries, contracts, clients, and regulators may require different cybersecurity and compliance standards. Popper Tech Team helps organizations align technology controls, security practices, documentation, and evidence with applicable requirements.
NIST Cybersecurity Framework
Structured cybersecurity practices for understanding, assessing, prioritizing, and communicating cybersecurity risk.
CMMC
Cybersecurity requirements that may apply to organizations working within the U.S. defense ecosystem and handling controlled information.
HIPAA
Security and privacy responsibilities for covered entities and business associates protecting electronic protected health information.
NYS DFS Part 500
Cybersecurity requirements applicable to certain New York-regulated financial organizations.
TeamCare Compliance supports readiness and alignment. It does not replace legal, regulatory, or certification advice.
A continuous process, not a one-time project.
Compliance becomes easier to manage when there is a clear process behind it.
Assess
Review the environment, controls, requirements, documentation, and known gaps.
Align
Map existing controls and practices against the relevant standard or requirement.
Remediate
Address priority gaps in security, access, configuration, documentation, or processes.
Document
Maintain policies, reports, records, and evidence that show how controls are managed.
Monitor
Continue monitoring security controls, risks, access, vulnerabilities, and changes.
Review
Keep controls, documentation, and business practices aligned as the organization changes.
Be ready before someone asks for the evidence.
Audits and compliance reviews become difficult when teams have to reconstruct months of activity after the fact.
Maintain the evidence during normal operations instead of searching for it when the audit begins.
More confidence. Fewer surprises.
A well-managed compliance program should make responsibilities clearer, not create constant uncertainty.
Clearer Responsibilities
Leadership understands what needs to be maintained and where accountability sits.
Better Documentation
Policies, evidence, reports, and records are easier to manage and locate.
Fewer Audit Surprises
Gaps can be identified during ongoing reviews instead of at the last minute.
Stronger Security
Compliance is supported by the same cybersecurity foundation used to protect the environment.
Better Visibility
Leadership gets clearer insight into risk, gaps, remediation priorities, and readiness.
Less Administrative Pressure
Compliance becomes part of normal IT operations rather than a recurring emergency.
Built for organizations that need to protect it and prove it.
TeamCare Compliance is designed for organizations where cybersecurity responsibilities extend beyond basic protection.
Financial & Advisory Firms
Support regulatory, security, and documentation responsibilities across sensitive financial environments.
Regulated Professional Organizations
Strengthen processes around controls, documentation, evidence, and ongoing readiness.
Firms Preparing for Audits or Reviews
Maintain policies, evidence, logs, and security documentation more continuously.
Growing Businesses
Manage compliance responsibilities more consistently as employees, vendors, systems, and clients increase.
Start with the responsibility your business has.
Stay Ready
Are You Ready to Show How Your Security Is Being Managed?
If preparing for compliance means searching for documents, rebuilding records, or trying to understand your controls at the last minute, there is a better approach.
Clear requirements. Practical priorities. Better audit readiness.